Every wave of new technology arrives first through the side door. With AI it arrived fast. Microsoft's 2024 Work Trend Index found that 75% of knowledge workers used AI at work and 78% of AI users brought their own AI tools [2].
Bring-your-own chat was a data-leak risk. Bring-your-own agent is different in kind. An agent connected to someone's mailbox, drive or code host acts with that person's own tokens. To every system it touches, it looks exactly like them. It does not show up in an inventory, and nobody reviewed its permissions because, technically, nobody granted any new ones.
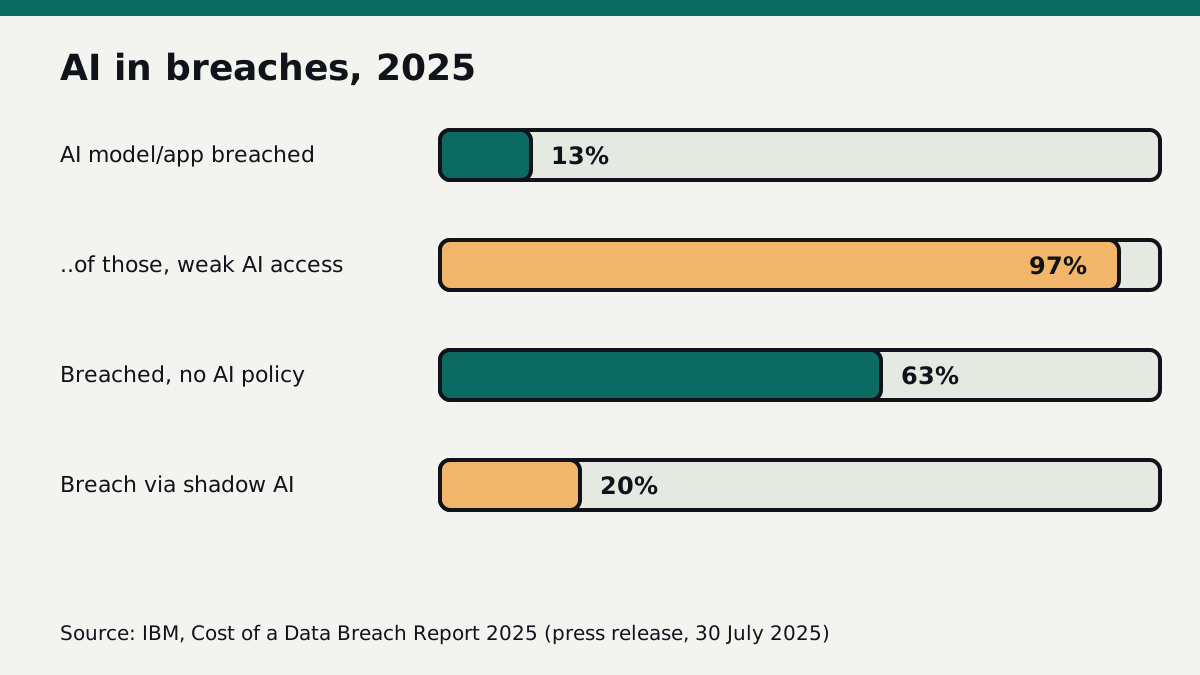
The cost is now measured. IBM's 2025 breach research found that one in five organizations reported a breach due to shadow AI, and those with high levels of shadow AI saw an average of $670,000 in higher breach costs. The same report found that 13% of organizations reported breaches of AI models or applications, 97% of those lacked proper AI access controls, and 63% of breached organizations had no AI governance policy or were still writing one [1].
Banning the tools rarely works; people route around bans when the tools save them hours. What works is giving them a sanctioned path that is easier than the shadow one, and making agent access visible.
What to do about it
Find the agents first: review OAuth grants and API tokens issued to AI tools, then move the useful ones onto their own scoped service identities with logging. Our Govern service puts scoped credentials, audit trails and stop controls around your agents. See Govern.